
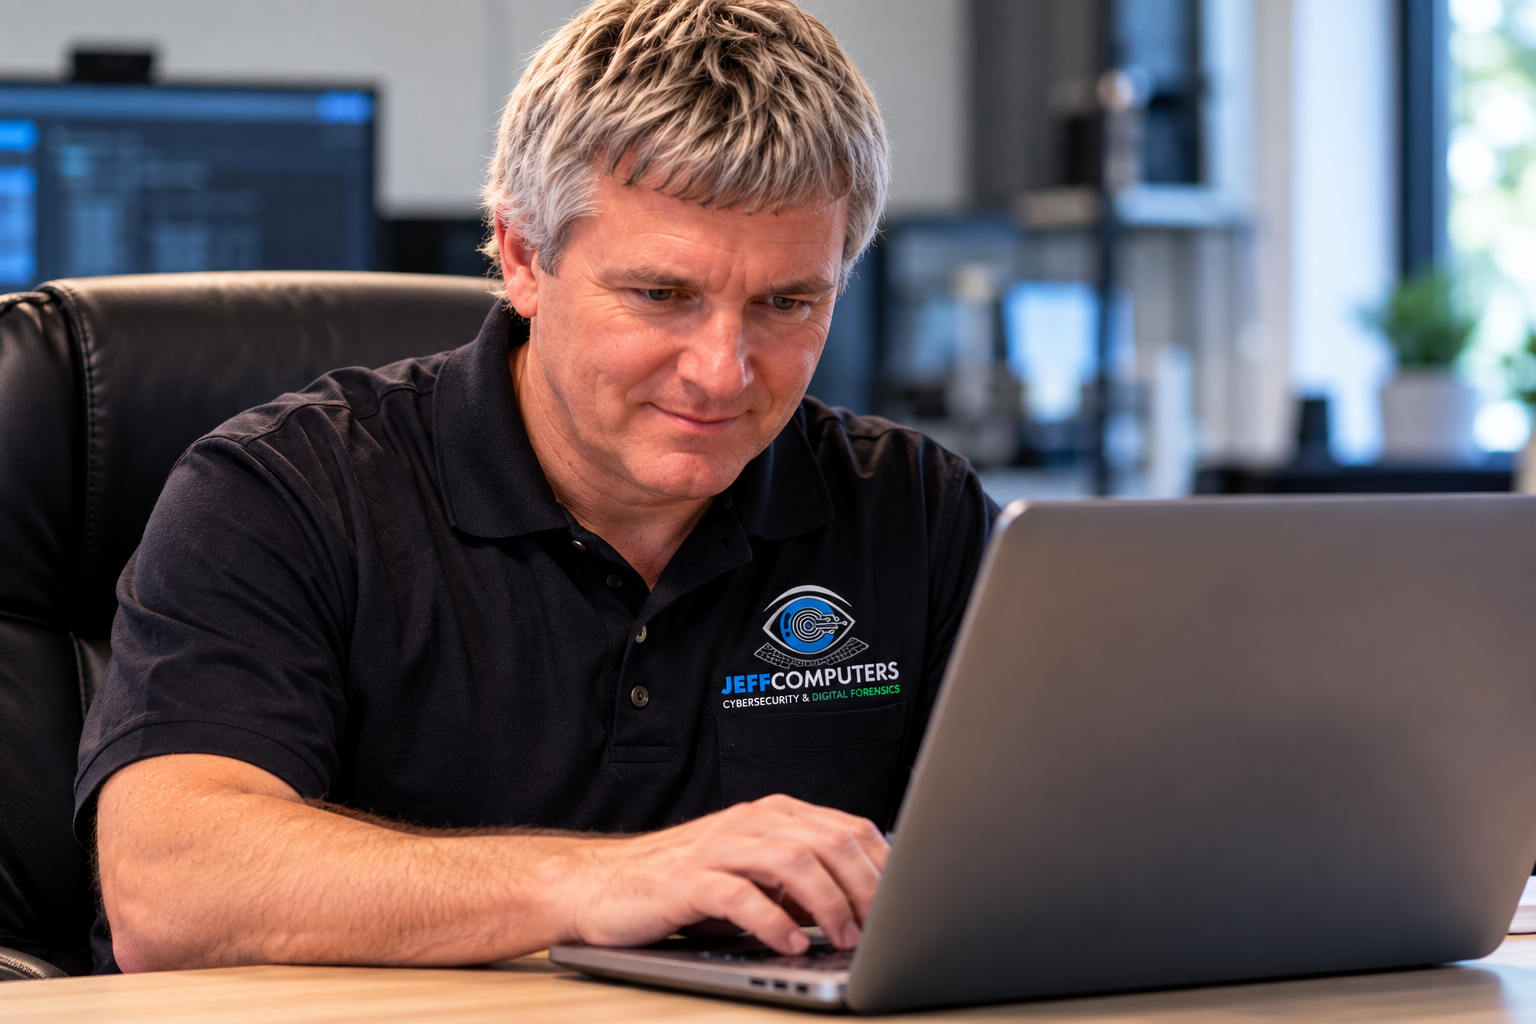
A computer that suddenly slows down, opens unfamiliar websites, or displays repeated warnings can be frustrating. Not every performance problem means the machine is infected, but some symptoms deserve prompt investigation. The most useful first step is to separate an ordinary technical issue from a possible security incident and avoid actions that could make the situation worse.
Recognize the warning signs
Common signs of trouble include browser redirects to pages you did not request, unwanted extensions, login alerts from unfamiliar locations, and antivirus software that has unexpectedly stopped working. Files with unfamiliar extensions or a ransom note are more urgent signs. A noisy fan or a slow startup alone does not prove malware; background updates, storage problems, and aging hardware can cause similar symptoms.
Look at the whole pattern rather than one isolated warning. Ask when the behavior started and whether it followed a software installation, attachment download, or suspicious message. Those details may help a technician determine what happened.
Disconnect when compromise seems likely
If you see active remote-control behavior, ransomware messages, or signs that files are being accessed without your permission, disconnect the device from Wi-Fi or unplug its network cable. This can help reduce ongoing communication with an attacker. If it is a work computer, contact the organization's IT contact promptly and follow its incident procedures. Do not begin deleting suspicious files or resetting the computer before relevant evidence and important data have been considered.
If the incident involves a bank account or payment card, use a different trusted device to contact the financial institution directly. Avoid calling numbers shown in pop-up warnings, which may be part of a tech-support scam.
Protect accounts from a clean device
On a different device that you trust, change the passwords for important accounts, starting with email, banking, and the password manager. Use a unique password for each account and enable multifactor authentication. Review recovery email addresses, account sessions, forwarding rules, and recent sign-in activity. A password reset is not enough if an attacker has changed recovery settings or added an unauthorized sign-in method.
If personal or work information may have been exposed, document what happened and decide whether additional reporting is required. Business owners may need to follow incident response, insurance, client notification, or regulatory procedures depending on the facts.
Scan and investigate carefully
Use reputable security software that is already installed or obtained from the vendor's official website. Update the security definitions before scanning when it is safe to reconnect. Avoid installing multiple unknown cleaners advertised through urgent pop-ups; some are themselves unwanted software. A full scan may identify familiar threats, but it cannot guarantee that all forms of compromise have been removed.
For an infected browser, inspect extensions, notification permissions, startup pages, and search engine settings. Remove only items you can identify as unauthorized. If the device handles sensitive business information, a professional assessment is often preferable to guessing which files can be safely removed.
Know when expert help is useful
Seek professional help if you see repeated account compromise, ransomware, disabled security tools, or suspicious behavior that returns after cleanup. The same applies when important files could be lost. For homeowners and small businesses around Osprey and Sarasota, Jeff Computers offers professional virus and malware removal, including diagnosis and recovery-oriented guidance. The objective should be to determine what changed, remove the threat, and address the vulnerability that allowed it in.
Prevent the next incident
Once the device is trustworthy, turn on automatic software updates, use multifactor authentication, and maintain backups that can be restored independently of the original device. Test a backup occasionally; an untested backup is an assumption, not a recovery plan. Teach everyone who uses the computer to recognize fake security alerts and urgent payment requests.
A suspicious computer does not always indicate a major breach. Treat unusual behavior seriously, preserve critical information, and use a measured investigation rather than following the first warning on the screen. That approach protects both your data and your ability to recover.

Responses (0)